

INFORMATION communications technology (ICT) personnel of all banks should be burning midnight oil or on high alert this weekend after the Bank Rakyat’s corporate portal http://iRakyat.com.my was hacked into – probably a testament that claims of cyberattack being on the rise in Malaysia is no hoax.
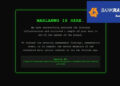
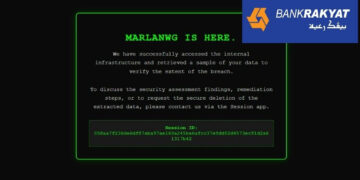
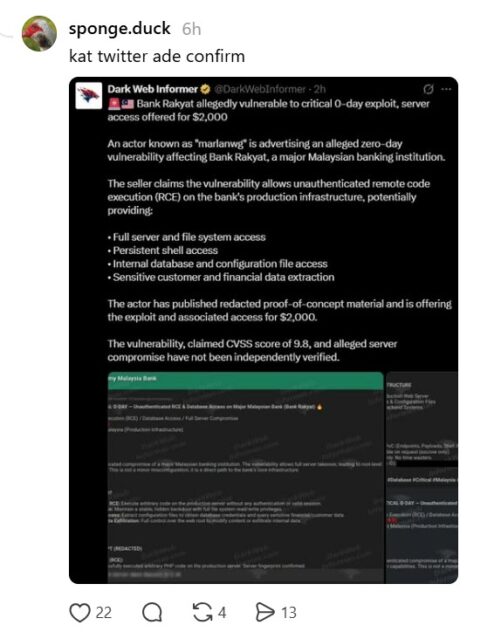
This follows a viral screenshot of Bank Rakyat’s defaced website depicting a message “MARLANWG IS HERE” alongside claims that the threat actor/hacker has accessed the bank’s internal infrastructure and stole sample data while seeking to contact via the Session app.
“@mybankrakyat has been hacked … just want to wish good luck to its IT team tonight. 🫡🫡” penned software engineer nep (@imalanep_) on Threads with his one-liner post having garnered 9.5K likes, 228 comments, 846 re-posts and 3K shares at the time of writing.
Editor’s Note: Bank Rakyat has confirmed that its corporate portal has reportedly experiencing a temporary access disruption.
Through a notification on its official Facebook page, the bank advised customers to use alternative digital channels and mobile applications to continue their banking transactions.
Among the recommended platforms are the iRakyat mobile banking application, BRICK, QR2E and the i-bizRAKYAT business banking portal.
“We apologise for any inconvenience caused. Thank you for your patience,” read a brief statement issued by the banking institution at about 11.30 pm last night (Nov 7).
The latest incidence of hacking which apparently is not Bank Rakyat’s first has sent shivers down the spine of fellow Threader Ezmir Danial (@ezmirdanial).
“Not trying to be scaremonger but if even Bank Rakyat itself can be hacked by ‘Marlanwg’, saving money in the bank is not entirely safe,” asserted the self-proclaimed real estate advisor.
“Should we cash out and put our money under the mattress? 😭”
Elsewhere, a presumably Indonesia-based finfluencer HakaHaki (@hakahaki_id) claimed that the said hacker has “already sold Bank Rakyat’s data on darkweb”.
“HakaHaki team has verified the samples shared by the user ‘marlanwg’ and confirmed that the data appears to be authentic,” validated the Threader.
Editor’s Note: Recall that Bank Negara Malaysia (BNM) has previously penalised Bank Rakyat with a RM1 mil administrative monetary penalty under the Risk Management in Technology (RMiT) framework following a separate cybersecurity breach in January this year.
To-date, Bank Rakyat has yet to issue a formal public statement or announce explicit actions regarding the validity of the hacker’s internal access claims.
Until a formal statement has been made, Bank Rakyat customers are advised not to enter sensitive details to avoid potential phishing attacks.
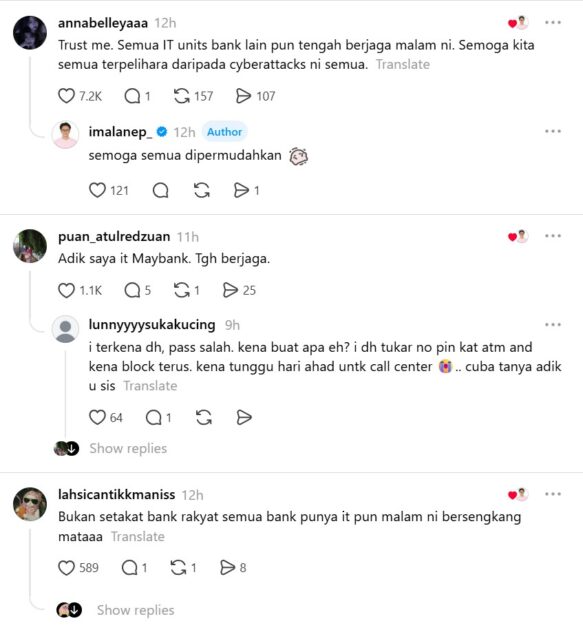
As concerns abound about vulnerability of the cybersecurity level of home-grown banks, many commenters were seemingly optimistic that “all other IT units in local bank are on guard tonight” with one confirming that “my brother at Maybank, too, is on guard”.
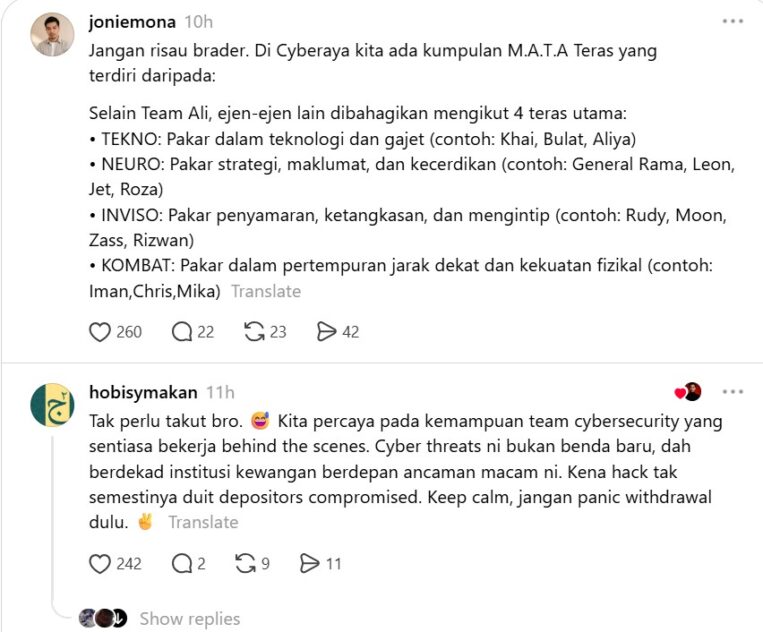
Beyond financial institutions, one seemingly insightful commenter revealed that there is even a Cyberjaya-based “M.A.T.A Teras group” to protect Malaysia from any wide scale cyberattack.
“n addition to Team Ali, other agents are divided into four main pillars,” shared the self-proclaimed “property matchmaker 🏡”.
“They comprised:
-
TEKNO: Experts in technology and gadgets (eg, Khai, Bulat, Aliya)
-
NEURO: Experts in strategy, information and intelligence (eg General Rama, Leon, Jet, Roza)
-
INVISO: Experts in disguise, agility and espionage (eg Rudy, Moon, Zass, Rizwan)
-
KOMBAT: Experts in close combat and physical strength (eg Iman, Chris, Mika).
This is when some cheeky commenters openly declared that “it’s (cyberattack) fine so long as our debts are wiped out but not our savings lost”. – Nov 7, 2026